What Is Network Segmentation and Why Does It Matter for Cybersecurity? – Complete 2026 Guide

Picture an office with no inside walls at all, one huge, open room with no doors. If a fire starts in one corner, nothing stops it from spreading through the whole space.

Network segmentation builds those missing walls back into your IT setup. This guide explains what segmentation is, why it matters so much for safety, and how your firm can start using it.

Lagos Data School made this guide as part of our hands-on cyber course. Indeed, segmentation forms a core part of nearly every defense plan we teach. So let’s break it down clearly.


What Is Network Segmentation?

Network segmentation means splitting a single, large network into smaller, separate parts, often called zones or segments. Each zone can have its own rules for who and what may enter.

This may contain: networked devices connected to each other with the words network segmentation above them

Think back to the office example. Instead of one open room, segmentation adds walls and locked doors between departments. So if trouble starts in one room, it does not spread freely into the next.

In a digital network, this might mean keeping your finance systems on one segment, your general staff devices on another, and your guest Wi-Fi on a third, fully separate zone.


How Network Segmentation Works

Segmentation uses tools like firewalls, switches, and special software rules to control traffic between zones. Each zone acts almost like its own small network, even though all the zones still belong to the same larger firm.

Traffic that wants to move from one zone to another must pass through a checkpoint, often a firewall, that decides if the move is allowed. This checkpoint can block, allow, or watch closely any traffic that tries to cross zone lines.

As a result, even a fully trusted user on one zone may still face limits when trying to reach a different, more sensitive zone elsewhere in the network.


Why Network Segmentation Matters So Much

Segmentation matters because it directly limits the harm a single breach can cause. Without it, one weak point can open the door to your entire network at once.

It Stops Attacks From Spreading

If a hacker breaks into one segment, strong walls stop them from moving freely into others. This buys your team real time to spot and stop the attack before it grows much larger.

It Protects Your Most Sensitive Data

By placing your most prized data, client records, money systems in their own tightly guarded zone, you add a real, extra layer of defense around what matters most.

It Helps You Meet Rule Requirements

Many rule bodies now want firms to show clear gaps between sensitive systems and normal staff use. Segmentation gives a clear, easy way to prove this gap during a check.

It Makes Problems Easier to Find

When something goes wrong in a smaller, well-defined zone, it is far easier to spot and fix than when the same problem hides somewhere within one huge, open network.


Types of Network Segmentation

There is more than one way to split up a network. Here are the main types that Nigerian IT teams should know.

Physical Segmentation

This method uses separate physical gear, different cables, switches, or even buildings to fully split networks apart. It offers strong safety but can cost more and take more space to set up.

Logical Segmentation (VLANs)

This method uses software rules to split a network into separate zones, even while sharing the same physical cables and gear. It costs less than physical segmentation and remains far more common in most firms today.

Micro-Segmentation

This is a newer, more detailed method that splits a network down to the level of single apps or even single workloads, rather than whole departments. It gives very fine, tight control, often used in larger firms with complex cloud setups.

As more Nigerian firms shift work onto cloud platforms, micro-segmentation is growing in real use, since cloud systems often run many small, separate workloads side by side that each need their own, tightly tuned set of access rules.


Network Segmentation and Zero Trust

Segmentation pairs closely with the growing Zero Trust security model that more Nigerian firms now adopt. In fact, segmentation forms one of the core building blocks that makes Zero Trust possible at all.

Without clear zones in place, it becomes far harder to apply strict, narrow access rules the way Zero Trust demands. So firms moving toward Zero Trust almost always start their journey with a fresh look at how their network is segmented.


How to Plan Your Own Network Segmentation

Lagos Data School teaches a clear, step-by-step path for firms looking to add or improve their own network segmentation.

Step 1: Map Your Current Network

Before you can split anything, you need a clear picture of what you already have. List your devices, servers, and how data currently flows between them.

Step 2: Group Assets by Sensitivity

Sort your systems by how sensitive or important they are. Finance and client data systems should sit apart from general staff tools like shared printers or basic file storage.

Step 3: Define Clear Zone Rules

For each zone, decide exactly what traffic should be allowed in and out. Write these rules down clearly, so anyone on your team can understand and check them later.

Step 4: Set Up Checkpoints Between Zones

Place firewalls or similar tools at each point where one zone connects to another. These checkpoints enforce the rules you defined in the step before.

Step 5: Test and Monitor Constantly

Once your zones are live, test that the rules work as planned. Then, keep watching traffic between zones over time, since needs and risks will shift as your firm grows and changes.


Common Mistakes Firms Make With Segmentation

Even well-meant segmentation plans can fall short if a few common mistakes creep in. Here is what Lagos Data School warns students to watch for.

Making Too Many Tiny Zones

Some firms split their network into far too many small zones, which becomes hard to manage well over time. Aim for a balance that gives real safety without making daily IT work too complex to handle.

Forgetting to Update Rules Over Time

As staff roles change and new tools get added, zone rules can grow outdated fast. So review your segmentation rules on a steady, repeat schedule, not just once at the start.

Leaving Old Devices Unassigned

Older devices can get left out of the plan, often by simple mistake. These forgotten devices can quietly turn into weak spots that slip past your whole careful setup.


Network Segmentation for Small Nigerian Businesses

Many small firms wrongly think segmentation only suits large banks or big firms with deep budgets. In truth, even a small firm with under twenty staff can benefit greatly from some basic level of segmentation.

A simple starting point might be splitting guest Wi-Fi from staff Wi-Fi, then placing any system that holds client payment data on its own separate, tightly guarded zone. These small first steps can be done with low cost, using tools many small firms already own.

Lagos Data School works close with small firm owners to build plans that fit a tight budget, without giving up the core safety this step brings.


Recommended External Resource

For an official guide on network segmentation, visit the CISA cybersecurity resource page: https://www.cisa.gov/topics/cybersecurity-best-practices


A Real-World Example: A Nigerian Hospital Network

To picture this more clearly, think about a busy hospital in Lagos. Without segmentation, a single network might link patient record systems, staff laptops, guest Wi-Fi, and even medical devices like heart monitors, all in one open space.

If a hacker broke into the guest Wi-Fi through a weak password, an unsegmented network would let them move freely toward far more sensitive systems, including patient records or even connected medical gear.

With proper segmentation in place, that same hacker would hit a wall right after the guest zone. Patient records would sit in their own tightly guarded zone, and medical devices would sit in another, fully separate from general staff or guest traffic.

This kind of setup can be the difference between a minor, contained incident and a major breach that puts patient safety and trust at real risk. Lagos Data School uses examples like this to help students see why segmentation matters well beyond pure theory.


Segmentation and Cost Savings Over Time

Beyond pure safety, segmentation can also save Nigerian firms real money over time, in ways that may not be obvious at first glance.

When a breach does happen, a well-segmented network often limits the damage to one small zone, rather than the entire firm. This can mean far lower cleanup costs, less downtime, and far less harm to client trust compared to a full, firm-wide breach.

Furthermore, segmentation can make your network easier to manage day to day, since IT staff can focus their closest attention on the most sensitive zones, rather than spreading limited time and care evenly across one giant, undivided network.

So while segmentation does take upfront effort and some cost to set up well, many Nigerian firms find that it pays for itself many times over, the very first time it helps contain what could have been a much larger, costlier breach.

Also, a clean, well-split network tends to run faster too, since less traffic competes for space in any one part of the system. So segmentation can bring a small speed gain on top of its safety value, which firms do not always expect at first.

Over a few years, these small gains in speed and in lower breach costs can add up to a real, clear return on the time your firm spent setting segmentation up well in the first place.


Segmentation Readiness Self-Check

Before you close this guide, run through this short self-check to see how ready your firm is to start or improve segmentation.

  • Do you have a full map of your devices and how they connect today?
  • Is your guest Wi-Fi split apart from your main staff network?
  • Does your most sensitive data sit in its own guarded zone?
  • Do you check your zone rules at least once a year?
  • Could one weak device today put your whole network at risk?

If your answer to the last question is yes, segmentation should sit near the top of your firm’s safety plan this year. Lagos Data School built this self-check from real gaps we see often when we train Nigerian IT staff and small firm owners.


About Lagos Data School

Lagos Data School is Nigeria’s top school for cyber security, data science, cloud, and analytics. Every idea in this guide is part of our hands-on course.

Our teachers are real security pros, not just classroom staff. So you learn from people who guard live networks every day.

We run classes on weekdays, weekends, and online. So no matter your time, we have a slot for you. Beyond skills, we also give you a real certificate and links to job partners.

Visit Lagos Data School today to view our courses and join the next class.

Build walls that hold. Train with Lagos Data School.
How to Perform a Network Security Audit for a Small Business

Most small firms in Nigeria run their IT setup for months, or even years, with no real check on how safe it truly is. This gap can leave real risk sitting in plain sight, unseen until it is far too late.

A network security audit is the fix for this gap. It is a clear, step-by-step check of your whole IT setup, built to find weak spots before a hacker does.

This guide walks you through running your own audit, even with a small team and a tight budget. Lagos Data School built this same process into our hands-on cyber course, so let’s walk through it now.


What Is a Network Security Audit?

A network security audit is a comprehensive review of your firm’s IT infrastructure, aimed at identifying vulnerabilities, gaps, and risks. It looks at your gear, your software, your rules, and even how your staff uses your systems each day.

Story pin image

Think of it like a health check at the doctor. Even if you feel fine, a check can catch small issues before they grow into big, costly ones. A security audit works the same way for your network.

Many firms wait until after a breach to run their first real audit. But the smart move is to run one before trouble hits, not after the damage is done.


Why Small Businesses in Nigeria Need Regular Audits

Many small firms wrongly think hackers only target big banks or large firms. But in truth, small firms are often seen as easier targets, since they tend to have weaker defenses in place.

Furthermore, a single breach can hit a small firm far harder than a large one, since small firms rarely have the funds to bounce back fast from a major loss. Also, more clients now ask small firms about their safety steps before they agree to work together.

So a regular audit is not just a tech task; it is a real step toward keeping your firm alive and trusted in a tough, fast-moving market.


Step-by-Step Guide to a Network Security Audit

Here is the clear, step-by-step plan that Lagos Data School teaches for running your own audit, even as a small firm with limited staff.

Step 1: Define the Scope of Your Audit

First, decide what your audit will cover. Will it check your whole network, or just one key part, like your client data store? Setting clear limits up front helps keep your audit on track and easy to manage.

Step 2: List All Your Assets

Next, write down every device, server, and tool your firm uses. This list should cover laptops, phones, routers, cloud tools, and any software that holds firm or client data.

You can not guard what you do not know you have. So this step, though simple, often reveals gear or tools that staff use without IT’s full knowledge.

Step 3: Check Your Firewall and Network Setup

Review your firewall rules to confirm they still make sense. Look for old rules tied to staff who have left, or tools no longer in use. A firewall full of outdated rules can hide real gaps from view.

Step 4: Review User Access and Passwords

Check who has access to what within your systems. Ask if each staff member truly needs the level of access they currently hold, or if it should be cut back.

Also, check your password rules. Weak or shared passwords remain one of the most common ways that hackers break into small firms with ease.

Step 5: Check for Missing Software Updates

Outdated software often carries known flaws that hackers can use to break in. So check that all your software, from your router’s firmware to your office apps, runs on its latest version.

Step 6: Test Your Wi-Fi Security

Confirm your office Wi-Fi uses a strong lock type, like WPA3 or WPA2, and that your password is strong. Also, confirm that guest devices sit on a separate network from your main staff systems.

Step 7: Review Your Backup Systems

Check that your firm backs up key data on a regular plan, and that those backups actually work when tested. A backup that fails to restore properly gives you false comfort, not real safety.

Step 8: Look for Signs of Past Breaches

Check your logs, where they exist, for any signs of past odd activity. This step can reveal a breach that went unnoticed at the time it happened, which is more common than most firms realize.

Step 9: Test Your Staff’s Security Awareness

Run a simple test, such as a mock phishing email, to see how staff respond. This step often reveals more risk than any single piece of software ever could.

Step 10: Document Your Findings and Build an Action Plan

Write down every issue you find, no matter how small it may seem. Then, rank each one by how serious it is, and build a clear plan for who will fix what, and by when.


Tools That Help With a Small Business Audit

You do not need a huge budget to run a solid audit. Many free or low-cost tools can support each step of the process.

  • Wireshark for a close look at your live network traffic
  • Nmap for scanning your network to find open, unguarded ports
  • A password manager for checking and improving staff password habits
  • A free phishing test service for checking staff awareness in a safe way

Lagos Data School trains students to use tools like these directly within our hands-on labs, so graduates can run a real audit from day one in their first job.


How Often Should a Small Business Run an Audit?

There is no single right answer, since it depends on your firm’s size and risk level. However, Lagos Data School suggests a clear, simple rule for most small Nigerian firms.

Run a full, deep audit once a year, at a minimum. Run a smaller, lighter check every quarter, to catch any fast-changing risks between your full audits.

Also, run an extra audit any time something major changes, a new office, a new core tool, or a big rise in staff count. Change often brings new risk that an old audit would not have caught.


What to Do With Your Audit Results

Finding issues is only half the job. The real value comes from what you do next with what you have found.

First, fix the most serious issues first, not the easiest ones. A small, simple fix can wait if a much larger risk sits unattended nearby.

Next, assign clear owners to each fix, with a real deadline attached. An issue with no owner and no date often never gets fixed at all.

Finally, keep a written record of each audit and its results over time. This record helps you track real progress, and it can also prove useful if a client or partner ever asks about your firm’s safety history.


Common Mistakes Small Firms Make During Audits

Even well-meant audits can fall short if a few common mistakes creep in. Here is what Lagos Data School warns students to watch for.

Treating the Audit as a One-Time Event

Some firms run one audit, fix a few issues, then never look again. But threats change fast, so a single audit can not protect you forever. Build audits into a regular, repeat habit instead.

Ignoring Small Issues

A small gap may seem harmless on its own, but a hacker often chains many small gaps together to cause real harm. So do not skip a fix just because the issue seems minor at first glance.

Skipping Staff in the Process

Some audits focus only on tools and gear, while staff habits go unchecked. But staff actions cause a huge share of real breaches. So always include a real check on staff habits in your audit.


Building a Culture of Regular Security Checks

Beyond the audit steps themselves, the real goal is to build a firm-wide habit of care around safety. This means talking about safety in normal team meetings, not just during a yearly review.

It also means making it easy and safe for staff to report odd activity, without fear of blame. Often, a staff member spots something odd well before any tool does but only if they feel free to speak up.

Lagos Data School works to instill this exact mindset in every student, since strong tools matter less without a strong, alert team standing behind them.


Recommended External Resource

For an official audit framework, visit the NIST Cybersecurity Framework guide: https://www.nist.gov/cyberframework


Should You Hire an Outside Firm for Your Audit?

Some small firms choose to run their own audit in-house, while others bring in an outside firm to do the work for them. Both paths have real merit, depending on your own firm’s needs and budget.

Running your own audit costs less and helps your in-house team build real skill over time. This route suits firms with at least one staff member who has some grasp of IT and security basics already in place.

Hiring an outside firm often costs more, but it brings a fresh, outside view that may catch things your own team has grown too used to seeing each day. An outside firm also tends to have deeper tools and more hands-on field experience across many different firms.

Many small Nigerian firms choose a mixed route. They run light, in-house checks each quarter, then bring in an outside firm once a year for a deeper, more thorough review. Lagos Data School trains students to perform both kinds of audits, so they can serve firms either as an in-house hire or as an outside expert later in their career.


Preparing Your Team for the Audit Process

An audit goes far more smoothly when your whole team understands why it is happening and what role they play in it. So take time to explain the process to staff before you begin.

Make clear that the goal is to find and fix gaps, not to place blame on any one staff member for past mistakes. Staff who fear blame often hide facts or stay quiet, which can hide real risk from view during the audit.

Also, set clear timelines so staff know what is expected of them and by when. A vague, open-ended audit tends to drag on far longer than one with clear, firm deadlines attached to each step.

Lagos Data School stresses this human side of the audit process just as much as the technical steps, since even the best checklist fails if the people involved do not feel free to speak up and engage with it fully.


A Quick Audit Readiness Self-Check

Before you start your audit, run through this short self-check to see how ready your firm truly is.

  • Do you have a full, written list of all your firm’s devices and tools?
  • Do you know who has access to your most sensitive data right now?
  • Have you tested a backup restore within the past six months?
  • Does your team know how to spot and report a phishing attempt?
  • Do you have a clear plan for who fixes issues once the audit ends?

If you answered no to two or more of these, your firm has real, useful work to do before the next audit cycle begins. Lagos Data School built this self-check from real gaps we see most often when we train new IT staff and small firm owners.


About Lagos Data School

Lagos Data School is Nigeria’s top school for cybersecurity, data science, cloud, and analytics. Every idea in this guide is part of our hands-on course.

Our teachers are real security pros, not just classroom staff. So you learn from people who guard live networks every day.

We run classes on weekdays, weekends, and online. So no matter your time, we have a slot for you. Beyond skills, we also give you a real certificate and links to job partners.

Visit Lagos Data School today to view our courses and join the next class.

Find your gaps before hackers do. Train with Lagos Data School.

How to Set Up a Secure Wi-Fi Network for Your Office in Lagos: Complete 2026 Guide

Wi-Fi is the easiest way into your network for a bad actor. Unlike a cable, Wi-Fi signals pass through walls. So anyone close by could try to log in, even from the street outside your office.

In Lagos, this risk is even higher. Many office buildings sit close together. Also, shared workspaces often hold many firms on one floor. So locking down your Wi-Fi is a must, not a maybe.

Good news, this guide makes it simple. You will learn ten clear steps to lock down your office Wi-Fi. Each step is easy to do today, with tools you may already own.

Lagos Data School made this guide for IT staff and firm owners across Nigeria. We teach this same plan in our cyber training. So let’s start.


Why Office Wi-Fi Safety Matters in Lagos

Many Lagos firms still treat Wi-Fi as a simple plug-and-play tool. But this view leaves doors wide open for bad actors. A weak Wi-Fi setup can put your files, your cash, and your clients’ trust at risk.

Story pin image

Also, Lagos has many busy work zones: Victoria Island, Ikeja, Yaba, and more. In these spots, many networks overlap in range. So a hacker in a nearby cafe could try to break into a few firms at once.

So every firm, big or small, needs a clear plan for Wi-Fi safety. The steps below will help you build that plan from the start.


Step 1: Pick the Right Wi-Fi Type

Your router uses a type of lock to keep data safe. Old types are weak and easy to crack. New types are much safer. So check your router type before you set it up.


Wi-Fi Type How Safe Is It? What To Do
WEP Very weak. Easy to crack. Never use this
WPA Weak. Has known gaps. Switch right away
WPA2 Good. Used by most firms. Fine for now
WPA3 Strong. The newest type. Best pick in 2025


As you can see, WPA3 is the best pick today. If your router has it, turn it on now. If not, WPA2 will do for now, until you can buy a new router.


Step 2: Use a Strong, Hard-to-Guess Password

Skip simple words like your firm’s name or a phone number. Instead, pick a long phrase with letters, numbers, and signs mixed in. Also, change this password every few months.

This way, even an old leak does no harm down the line. Also, write your password rule down and share it with all staff. So everyone knows why a strong password counts.


Step 3: Split Guest and Staff Wi-Fi

Never let guests use the same Wi-Fi as your staff. Instead, set up a second network just for them, with its own password. So if a guest’s phone has a virus, it can not reach your real files.

Lagos firms see many guests each day: clients, vendors, and riders. So a guest network is one step that blocks a lot of risk. You can also limit how much data the guest network uses, which keeps your main speed fast.


Step 4: Rename and Hide Your Network

Change your Wi-Fi name from the one set at the factory. Do not use your firm’s name in it, since this makes you an easy target to spot. Also, turn off the public name list if your router allows it.

As a result, your network will not show up in nearby Wi-Fi lists. This small step adds a quiet layer of cover that many Lagos firms skip.


Step 5: Update Your Router Often

Router makers send out fixes for new bugs as they find them. But many Lagos firms never check for these fixes after the first setup. So set a date each month to check.

This one habit blocks many known attacks. Also, some routers can update on their own — so check your settings and turn this on if you can.


Step 6: Turn Off Remote Access

Most routers let you log in from anywhere online to change settings. But small offices rarely need this. So turn it off unless you truly need it.

If you leave it on, anyone in the world could try to break in. If you do need it, use a strong password and turn on two-step login if your router allows it.


Step 7: Add a Firewall Too

Wi-Fi locks are not enough on their own. A firewall adds a second wall of safety. It watches all traffic and can stop threats that slip past your Wi-Fi.


Step 8: Check Who Is Connected

Look at your router’s device list each week. If you see a device you do not know, act fast. Change your password right away and check it out.

This helps you catch trouble early, before it grows. Many new routers also send you a warning when a new device joins — turn this on if you can.


Step 9: Place Your Router in a Smart Spot

Where you place your router matters more than most people think. Keep it away from windows and outer walls. This way, your signal does not leak far into the street.

Also, put it in a central spot in your office. This gives even coverage across your space, with less waste. Lifting your router off the floor often helps both speed and range too.


Step 10: Set Up a Clear Wi-Fi Use Rule

Write a short, clear rule sheet for staff to follow. State which gear may join the work Wi-Fi and which should not. State what staff should avoid, such as sharing the password outside the office.

This way, everyone knows the rules from day one and not after a problem hits. Check this rule sheet once a year, since staff and gear change over time.


Common Wi-Fi Mistakes Lagos Offices Make

Even careful IT staff fall into common traps. Here are the slips Lagos Data School sees most, and how to avoid each one.

Leaving Factory Settings Untouched

Many routers still run on factory settings months after setup. This includes the admin password, which is often public on the web. So change every default setting on day one and not someday.

Using One Network for Everything

Some offices put staff, guests, and even smart gear like printers all on one network. As a result, one weak device can put the whole system at risk. So split your networks by use, where you can.

Skipping the Physical Side

Wi-Fi safety is not just a digital task. If anyone can walk up and reset your router, your rules mean little. So keep your router in a locked or limited area in your office.

Forgetting Smart Devices

Smart printers, cameras, and even office lights often join your Wi-Fi. But many of these come with weak security out of the box. So update their passwords and fixes just as well as you do your main router.


Why This Matters for Your Business

A safe Wi-Fi setup guards more than just your web link. It guards client data, money records, and your firm’s good name. Also, many clients now ask about your safety steps before they sign a deal.

So a well-locked office network can become a real plus for your firm and not just a tech task. Lagos Data School trains IT staff to see safety this way, as a key part of running a firm that people trust.


How Often Should You Review Your Wi-Fi Setup?

Setting up your Wi-Fi well is just the first step. You also need to check it over time, since threats and tools both change fast. So build a clear plan for how often you review each part.

Each week, check your list of joined devices for anything odd; each month, check for router fix packs and apply them right away; and each quarter, change your main Wi-Fi password, even if no issue has come up.

Each year, take a fresh look at your whole setup. By then, your staff list may have grown, your gear may have changed, and new risks may have come up that did not exist before. So a yearly deep check helps you stay one step ahead.

Lagos Data School builds this kind of review habit into every cyber course we run. We find that firms who check their setup on a fixed plan catch far more issues than those who wait until something breaks.


What to Do If You Suspect a Breach

Even with strong steps in place, no setup is fully safe from every risk. So you also need a clear plan for what to do if you think your Wi-Fi has been broken into.

First, change your Wi-Fi password right away, along with any admin login for the router itself. Next, check your device list for anything you do not know, and remove it from the network at once.

Then, look at your router logs, if your model keeps them, for signs of when the issue began. After that, update your router’s software fully, in case the break-in used a known flaw that a fix pack would have closed.

Finally, tell your staff what happened in plain terms, so they can also watch for odd signs on their own devices. Lagos Data School teaches this exact response plan as part of our hands-on training, so your team is ready before trouble strikes, not after.


Recommended External Resource

For an official guide on Wi-Fi safety, visit the Wi-Fi Alliance’s WPA3 page: https://www.wi-fi.org/discover-wi-fi/security


Wi-Fi Safety for Small Teams vs Large Firms

Not every office is the same size, so your Wi-Fi plan should fit your firm’s own needs. A small team of five may need far less than a large firm with two hundred staff.

For a small team, a single strong router with WPA3 and a good password may cover most needs. The steps in this guide are still worth doing, but the setup stays simple and quick to manage.

For a larger firm, you may need more than one router, spread out to cover the full space. You may also need a staff member whose main job is to watch and care for the network full time. In this case, a written rule sheet matters even more, since more staff means more chances for a slip to happen.

Either way, the core steps stay the same. Pick a strong lock type, use a strong password, split your networks by use, and check your setup often. Lagos Data School trains students to apply these same core ideas, no matter the size of the firm they work for.


Final Checklist Before You Go Live

Before you call your office Wi-Fi setup done, run through one last short check. This final pass helps catch any step you may have missed along the way.

  • Wi-Fi type is set to WPA3, or WPA2 if WPA3 is not yet on your gear
  • Password is long, mixed, and not tied to your firm’s name in any way
  • Guest network is split off from your main staff network fully
  • Network name does not show your firm’s name in plain text
  • Router firmware is fully up to date as of today
  • Remote access is off, unless you have a clear, real need for it
  • A firewall sits in place to back up your Wi-Fi defence
  • You know how to check your list of joined devices at any time

Once each box is checked, your office Wi-Fi stands in a far safer place than most firms in Lagos today. Lagos Data School built this checklist from real cases we have seen across many Nigerian firms, so use it as your final word before you call the job done.


About Lagos Data School

Lagos Data School is Nigeria’s top school for cybersecurity, data science, cloud, and analytics. Every idea in this guide is part of our hands-on course.

Our teachers are real security pros, not just classroom staff. So you learn from people who guard live networks every day.

We run classes on weekdays, weekends, and online. So no matter your time, we have a slot for you. Beyond skills, we also give you a real certificate and links to job partners.

Visit Lagos Data School today to view our courses and join the next class.

Secure your network. Train with Lagos Data School.


Web Application Penetration Testing: Complete 2026 Guide

Web applications are the most common attack target in Nigeria today. Furthermore, every fintech app, bank portal, and government system is at risk.

Lagos Data School teaches web application pen testing in its live cybersecurity course. Therefore, this guide explains the full methodology in clear, practical steps.

Also, Nigerian examples and free tools are included throughout. By the end, you will know how to conduct a professional web app assessment.


What Is Web Application Penetration Testing?

Web application penetration testing is a structured security assessment. Furthermore, it simulates real attacks on websites, APIs, and web portals. The goal is to find vulnerabilities before malicious attackers exploit them. Also, every finding is documented in a professional pen test report.

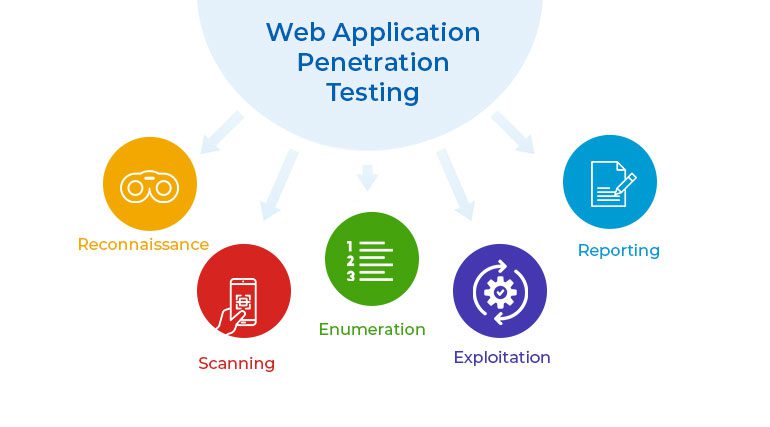
Guide for Web Application Penetration Testing

Consequently, the organisation fixes real security gaps with clear guidance. In short, web app pen testing protects Nigerian users and business data.


Why Nigerian Web Applications Are Vulnerable

Many Nigerian web applications are built quickly without security reviews. Furthermore, developers often prioritise features over secure coding practices. Also, third-party libraries are frequently outdated and carry known vulnerabilities.

Consequently, Nigerian fintech, e-commerce, and government portals face real risk. Therefore, every Nigerian web application needs regular professional pen testing.


The OWASP Top 10: The Foundation of Web App Pen Testing

The OWASP Top 10 is the global standard reference for web vulnerabilities. Visit OWASP.org for the full list. Furthermore, it lists the ten most critical web application security risks. Every professional web app pen test covers the OWASP Top 10 completely.

Also, Nigerian clients expect an OWASP-aligned report from every security firm. Consequently, mastering the OWASP Top 10 is the foundation of this entire field.


The Top Five OWASP Risks Nigerian Ethical Hackers Must Know

Several OWASP risks appear most frequently on Nigerian web applications. Furthermore, each risk has its own testing technique and remediation approach.


  • Injection flaws: SQL, NoSQL, and command injection attack input fields.
  • Broken authentication: Weak login systems allow unauthorised account access.
  • Sensitive data exposure: Unencrypted data leaks through APIs or pages.
  • Insecure design flaws: Structural weaknesses that cannot be patched alone.
  • Security misconfiguration: Default settings leave servers and apps exposed.


In short, these five risks account for most Nigerian web app breaches. Consequently, testing for them first delivers the highest value to clients.


Tools Used in Web Application Penetration Testing

Professional web app pen testers rely on a core set of tools. Furthermore, each tool targets a different layer of the web application.


  • Burp Suite: Intercepts and modifies HTTP traffic between client and server.
  • OWASP ZAP: Free automated scanner for common web vulnerabilities.
  • SQLmap automates: Detection and exploitation of SQL injection flaws.
  • Nikto scans: Web servers for thousands of known misconfigurations.
  • Dirsearch finds: Hidden directories and files on web servers quickly.


Also, Burp Suite is the most essential tool on every web pen test. Consequently, Nigerian ethical hackers must master Burp Suite above all others.


The Step-by-Step Web App Pen Testing Methodology


Step 1: Pre-Engagement and Scope Agreement

Every professional web app pen test starts with a written scope agreement. Furthermore, the scope lists every URL, API, and function that can be tested. Also, out-of-scope items are listed explicitly to prevent legal issues.

Consequently, the ethical hacker is legally protected throughout the engagement. Therefore, never begin any testing before the scope document is signed.


Step 2: Passive Reconnaissance

Passive reconnaissance gathers information without directly touching the target. Furthermore, WHOIS records, DNS lookups, and Google dorking are used.

Also, Shodan is searched for exposed services linked to the target domain. Consequently, the ethical hacker builds a full picture of the target environment. Therefore, passive recon always precedes any active scanning or testing.


Step 3: Active Scanning and Enumeration

Active scanning sends requests directly to the target web application. Furthermore, Nikto and OWASP ZAP run automated scans on all pages.

Also, Dirsearch and Gobuster discover hidden directories and backup files. Consequently, a comprehensive list of attack surfaces is mapped completely. Therefore, active scanning reveals what passive recon cannot see at all.


Step 4: Manual Testing for OWASP Top 10 Vulnerabilities

Manual testing goes deeper than any automated scanner can reach. Furthermore, automated tools miss business logic flaws and complex IDOR bugs. Also, Burp Suite is used to intercept and manipulate every HTTP request.

Consequently, Nigerian ethical hackers find vulnerabilities that tools cannot detect. Therefore, manual testing is the most important phase of any web assessment.


How to Test for SQL Injection Manually

SQL injection testing starts with identifying every input field on the app. Furthermore, a single quote (‘) is entered in each input to test for errors. Also, an SQL error message in the response confirms a potential injection point.

Consequently, SQLmap is used to exploit confirmed injection points automatically. Therefore, every text field and search box must be tested for SQL injection.


How to Test for Cross-Site Scripting (XSS)

XSS testing injects JavaScript payloads into input fields and URL parameters. Furthermore, a simple payload like script>alert(1)/script reveals reflected XSS.

Also, stored XSS persists in the database and fires on every page load. Consequently, XSS vulnerabilities put every Nigerian user of the app at risk. Therefore, all text inputs and URL parameters must be tested for XSS carefully.


How to Test for Insecure Direct Object Reference (IDOR)

IDOR vulnerabilities allow access to other users’ data without authorisation. Furthermore, they are found by changing user IDs in URLs and API requests.

Also, Burp Suite’s Repeater tool makes IDOR testing fast and systematic. Consequently, Nigerian banking and fintech apps are frequently vulnerable to IDOR. Therefore, every user-specific endpoint must be tested for IDOR flaws.


Step 5: Authentication and Session Testing

Authentication testing verifies that login mechanisms are secure and robust. Furthermore, default credentials, brute-force resistance, and MFA are all tested.

Also, session tokens are inspected for randomness and proper expiry settings. Consequently, weak session management is one of the most commonly found flaws. Therefore, every Nigerian web app must have strong authentication and sessions.


Step 6: API Security Testing

Modern Nigerian web applications rely heavily on APIs for all data exchange. Furthermore, APIs often expose more data than the visible front end does.

Also, unauthenticated API endpoints are a very common Nigerian vulnerability. Consequently, all API endpoints must be enumerated and tested completely. Therefore, API testing is now as important as front-end web testing.


Step 7: Reporting and Remediation Guidance

Every web app pen test ends with a detailed, professional written report. Furthermore, findings are rated using CVSS scores from Critical to Informational.

Also, each finding includes clear steps to reproduce and fix the vulnerability. Consequently, Nigerian clients understand both the risk and the required action. Therefore, the report is the most valuable deliverable of the entire engagement.


A Nigerian Web App Pen Test Example

A Lagos e-commerce platform hires an ethical hacker for a full assessment. Furthermore, the scope covers the checkout flow, user accounts, and product API.

Passive recon reveals three subdomains not listed on the main website. Also, active scanning finds an exposed admin panel on one subdomain. Consequently, the ethical hacker accesses the panel using default credentials.

Next, a full OWASP Top 10 manual test reveals four additional vulnerabilities. Finally, a Critical report is delivered with a prioritised fix list. As a result, the client patches all findings within 30 days of receipt.


Web App Pen Testing Deliverables Every Nigerian Client Expects

Report Section Content
Executive Summary High-level overview for management and board
Scope and Methodology URLs tested, tools used, and assessment approach
Findings Summary Count of Critical, High, Medium, Low, and Info findings
Detailed Findings Each vulnerability with CVSS, evidence, and exploit steps
Remediation Guidance Specific fix recommendations ordered by risk priority
Re-test Schedule Timeline for verifying all fixes have been applied


Free Resource: OWASP Web Security Testing Guide

Lagos Data School recommends the OWASP Web Security Testing Guide as the definitive free reference. Furthermore, it covers every web vulnerability with detailed testing procedures.

Also, it is updated regularly by the global OWASP community. Consequently, Nigerian ethical hackers always have access to current testing guidance.


How Lagos Data School Teaches Web App Pen Testing

Lagos Data School covers the full web app pen testing methodology in its live course. Students practise every phase using Burp Suite, SQLmap, and OWASP ZAP. Furthermore, every lab exercise uses deliberately vulnerable Nigerian-style web apps.

Consequently, graduates conduct professional web app assessments from day one.

Visit the Lagos Data School training page to enrol today.

Frequently Asked Questions

Q1: How long does a web app pen test take in Nigeria?

A basic web app assessment takes three to five working days. Furthermore, complex applications with many endpoints take one to two weeks.

Also, the re-test phase adds an additional one to three days after fixes. Therefore, plan for one to three weeks total for a complete engagement.


Q2: Which certification covers web app pen testing best?

The OSCP and CEH both cover web application security testing in depth. Furthermore, PortSwigger’s free Web Security Academy is excellent preparation.

Also, the eWPT (eLearnSecurity Web Application Penetration Tester) is a specialist cert. Therefore, pursue eWPT if you want to specialise in web security specifically.


Q3: Can I practise web app pen testing for free?

Yes. DVWA, OWASP Juice Shop, and WebGoat are all free practice apps. Furthermore, PortSwigger Web Security Academy offers free guided web security labs.

Also, TryHackMe has dedicated web security learning paths for free. Consequently, Nigerian beginners have abundant free practice resources available.


Q4: Do Nigerian companies need web app pen tests?

Yes. The CBN and NITDA both require regular web security assessments. Furthermore, any Nigerian company storing customer data online has a legal obligation.

Also, international payment card standards (PCI DSS) mandate regular web pen tests. Consequently, web app pen testing is both a legal and a business necessity.


Q5: What is the difference between a web app scan and a pen test?

An automated scan identifies potential vulnerabilities without confirming exploitation. However, a pen test manually exploits and proves each vulnerability found.

Also, pen tests find business logic flaws and IDOR bugs that scanners miss. Therefore, a pen test always delivers more value than a scan alone.


Master Web App Pen Testing with Lagos Data School

Web application security is the most in-demand ethical hacking skill in Nigeria. Furthermore, every Nigerian company with a website needs this service regularly.

Lagos Data School trains you with live labs, real web app targets, and report writing.

Visit Lagos Data School and enrol in the cybersecurity course today.

Social Engineering Attacks: How Hackers Exploit Human Psychology

Most Nigerian cyberattacks begin with a human mistake, not a technical flaw. Furthermore, hackers know that people are easier to trick than computer systems.

Lagos Data School trains Nigerian professionals to recognise and resist social engineering. Therefore, this guide explains every major social engineering technique clearly.

Also, real Nigerian examples are used in every section. By the end, you will know how to protect yourself and your organisation.


What Is Social Engineering?

Social engineering is the art of manipulating people into revealing information. Furthermore, attackers exploit trust, fear, authority, and urgency to succeed. No technical hacking skill is required to run a social engineering attack.

This may contain: the word social engineering surrounded by hand drawn icons

Also, it is the most cost-effective attack method available to cybercriminals. Consequently, social engineering accounts for over 85% of all Nigerian cyberattacks. In short, the human mind is the most vulnerable system in any organisation.


Why Social Engineering Works So Well in Nigeria

Nigerian culture places high value on respect for authority and seniority. Furthermore, attackers exploit this by impersonating bosses and regulators.

Also, urgency tactics are effective in fast-paced Lagos work environments. Consequently, employees act before thinking when pressure is applied correctly. Therefore, social engineering defence must address Nigerian cultural dynamics.


The Six Principles Attackers Use to Manipulate Nigerians

Social engineers rely on six well-documented psychological principles. Furthermore, understanding these principles helps Nigerian staff resist manipulation.


  • Authority trigger: Impersonating a boss, regulator, or senior officer.
  • Urgency pressure: ‘Act now or your account will be closed immediately.’
  • Scarcity messaging: ‘Only you can approve this payment today.’
  • Social proof tactic: ‘Everyone else in your department already submitted.’
  • Liking exploitation: Building rapport before making a deceptive request.
  • Reciprocity trap: Doing a small favour first to create obligation.


In short, all six principles bypass rational thinking through emotion. Consequently, Nigerian staff make decisions they would never make calmly.


Type 1: Phishing Attacks

Phishing is the most common social engineering attack in Nigeria. Furthermore, deceptive emails are sent to trick recipients into acting. Links in phishing emails lead to fake login pages that steal credentials.

Also, attachments in phishing emails install malware on the victim’s device. Consequently, one successful phishing email can compromise an entire Nigerian bank. Therefore, every Nigerian professional must learn to identify phishing emails.


How to Recognise a Phishing Email in Nigeria

Several red flags appear in most phishing emails targeting Nigerian professionals. Furthermore, each flag is a learnable signal once you know what to look for.


  • Sender mismatch: The display name differs from the actual email address.
  • Urgency language: Phrases like ‘act immediately’ or ‘within 24 hours.’
  • Generic greeting: Emails start with ‘Dear Customer,’ not your real name.
  • Suspicious link: Hover over links; the URL looks wrong or misspelled.
  • Unexpected attachment: You receive a file you were not expecting at all.


Also, Nigerian banks and the EFCC never request passwords by email at all. Consequently, any email asking for credentials should be treated as phishing.


Real Nigerian Phishing Example: The Fake CBN Email

A fake email claiming to be from the CBN lands in a Lagos banker’s inbox. Furthermore, the email says: ‘Your BVN has been flagged — verify immediately.’

The link leads to a fake CBN portal that captures login credentials. Also, the email is sent from cbn-verify@gmail.com — not a real CBN domain.

Consequently, the banker’s credentials are stolen within minutes of clicking. Therefore, always check the sender domain before clicking any link at all.


Type 2: Spear Phishing

Spear phishing is a targeted version of regular phishing attacks. Furthermore, the attacker researches the victim on LinkedIn before attacking.

Also, the email references real names, projects, and Nigerian colleagues. Consequently, victims trust the email because it feels personally relevant. Therefore, spear phishing is far more dangerous than generic phishing attacks.


Nigerian Spear Phishing Example

A Nigerian CFO receives an email appearing to come from the CEO. Furthermore, the email says: ‘Please transfer ₦50m to our new vendor account. Also, the email references a real ongoing project the CFO is familiar with.

Consequently, the CFO transfers the funds without calling to verify the request. Therefore, this Business Email Compromise attack costs the company ₦50 million.


Type 3: Vishing (Voice Phishing)

Vishing attacks use phone calls instead of emails to deceive victims. Furthermore, attackers impersonate bank staff, EFCC officers, or IT support. Also, a spoofed caller ID makes the call appear to come from a real organisation.

Consequently, Nigerian victims share OTPs and passwords over the phone willingly. Therefore, never share passwords or OTPs on any unsolicited phone call.


Real Nigerian Vishing Example

A Nigerian POS merchant receives a call from ‘his bank’s fraud team.’ Furthermore, the caller says his card has been compromised and needs verification.

Also, the caller asks for his full card number and the OTP just sent. Consequently, the merchant shares both, and ₦200,000 is withdrawn immediately. Therefore, banks never call to ask for OTPs — hang up if this happens.


Type 4: Pretexting

Pretexting is creating a fabricated scenario to manipulate a target. Furthermore, the attacker builds a believable false identity before calling. Also, pretexts often claim authority — ‘I am from the Head Office IT team.’

Consequently, victims cooperate because the scenario feels entirely plausible. Therefore, Nigerian staff must verify any unusual request through official channels.


Pretexting in Nigerian Corporate Environments

An attacker calls a Nigerian bank’s helpdesk pretending to be the IT Director. Furthermore, he says a server is down and needs the admin password urgently.

Also, he references real internal system names to sound completely convincing. Consequently, the helpdesk agent resets and shares the admin password. Therefore, no password should ever be shared verbally over a phone call.


Type 5: Baiting

Baiting leaves infected USB drives in places Nigerian victims will find them. Furthermore, USB drives are labelled ‘Salary Spreadsheet Q3’ to tempt curiosity.

Also, plugging the drive installs keyloggers and remote access malware. Consequently, attackers gain access to the entire computer network silently. Therefore, Nigerian professionals should never plug in unverified USB drives.


Type 6: Tailgating and Physical Social Engineering

Tailgating is physically following an authorised person through a secure door. Furthermore, attackers dress professionally and carry large boxes to seem legitimate.

Also, Nigerian office staff hold doors open as a sign of politeness. Consequently, attackers gain physical access to Nigerian server rooms and offices. Therefore, always verify identity before allowing anyone through a secure door.


Social Engineering Attack Summary Table

Attack Type Method Nigerian Example Prevention
Phishing Fake email with malicious link Fake CBN BVN verification email Check sender domain — never click blindly
Spear Phishing Targeted email using personal data CEO fraud targeting Lagos CFO Verify large transfers via phone call
Vishing Phone call impersonation Bank fraud call requesting OTP Never share OTPs on any phone call
Pretexting Fabricated identity scenario IT Director impersonation at helpdesk Verify all requests through official channels
Baiting Infected physical media left as bait USB drive labelled ‘Salary Sheet Q3’ Never plug in unverified USB devices
Tailgating Physical entry through secure door Attacker follows staff into server room Always check identity at secure entry points


How Nigerian Organisations Defend Against Social Engineering

Defence requires both training and technical controls working together. Furthermore, neither alone is sufficient to stop determined attackers.


  • Security awareness training: Regular Nigerian staff training reduces click rates by 70%.
  • Phishing simulations: Controlled fake campaigns test real staff resilience.
  • Verify-before-you-act policy: All unusual requests need a second channel check.
  • Multi-factor authentication: MFA stops credential theft from succeeding fully.
  • Physical access controls: Tailgating is prevented with badge-only door access.


In short, a security-aware Nigerian workforce is the strongest defence. Consequently, training investment always delivers a measurable return in security.


Free Resource: SANS Social Engineering Defence Resources

Lagos Data School recommends the SANS Security Awareness resources as a free reference. Furthermore, they cover phishing defence, training programmes, and metrics.

Also, the SANS posters and tip sheets are free and available in PDF format. Consequently, Nigerian organisations can start staff training today at no cost.


How Lagos Data School Teaches Social Engineering Defence

Lagos Data School covers social engineering attack and defence in its cybersecurity course. Students learn to identify phishing, vishing, and pretexting techniques. Furthermore, live phishing simulation exercises are run in every cohort.

Consequently, graduates recognise social engineering attacks in their real workplaces.

Visit the Lagos Data School training page to enrol today.

Frequently Asked Questions

Q1: Is social engineering illegal in Nigeria?

Yes. Social engineering attacks are criminal offences under the Cybercrimes Act 2015. Furthermore, identity theft and financial fraud carry significant prison sentences.

Also, the EFCC actively prosecutes social engineering fraud in Lagos and Abuja. Therefore, Nigerian professionals must report suspected attacks to their IT team.


Q2: How can Nigerian staff recognise phishing emails?

Check the sender’s email domain carefully against the official company website. Furthermore, hover over every link before clicking to see the real URL.

Also, any email creating urgency about payments or accounts should be verified. Consequently, a simple two-second check prevents most successful phishing attacks.


Q3: Are Nigerian banks doing enough against social engineering?

Most tier-one Nigerian banks now run regular security awareness programmes. Furthermore, the CBN mandates cybersecurity training for all financial institution staff.

Also, SMS OTP notifications alert customers to suspicious account activity. Consequently, banks continue improving defences as attack techniques evolve.


Q4: What should a Nigerian employee do if they fall for a phishing attack?

Report the incident to your IT security team immediately without delay. Furthermore, change all passwords from a clean, uninfected device right away.

Also, alert your bank if financial accounts may have been compromised. Consequently, fast reporting limits the damage significantly for everyone involved.


Q5: Can social engineering be tested ethically in Nigeria?

Yes. Authorised social engineering tests — called red team exercises — are legal. Furthermore, Nigerian organisations use these to measure real employee resilience.

Also, Lagos Data School trains ethical hackers to conduct these tests professionally. Consequently, authorised testing identifies weaknesses before criminals exploit them.


Protect Your Nigerian Organisation with Lagos Data School

Social engineering is the number one entry point for Nigerian cyberattacks. Furthermore, technology alone cannot stop an attack that targets human trust.

Lagos Data School trains you to identify, test, and defend against every social engineering technique.

Visit Lagos Data School and enrol in the cybersecurity course today.

Hi, How Can We Help You?
Welcome To
Lagos Data School

Artificial Intelligence (AI), Machine Learning and Robotics Programmes Are Now Available!!!

Enroll Now!

Thank You
100% secure website.